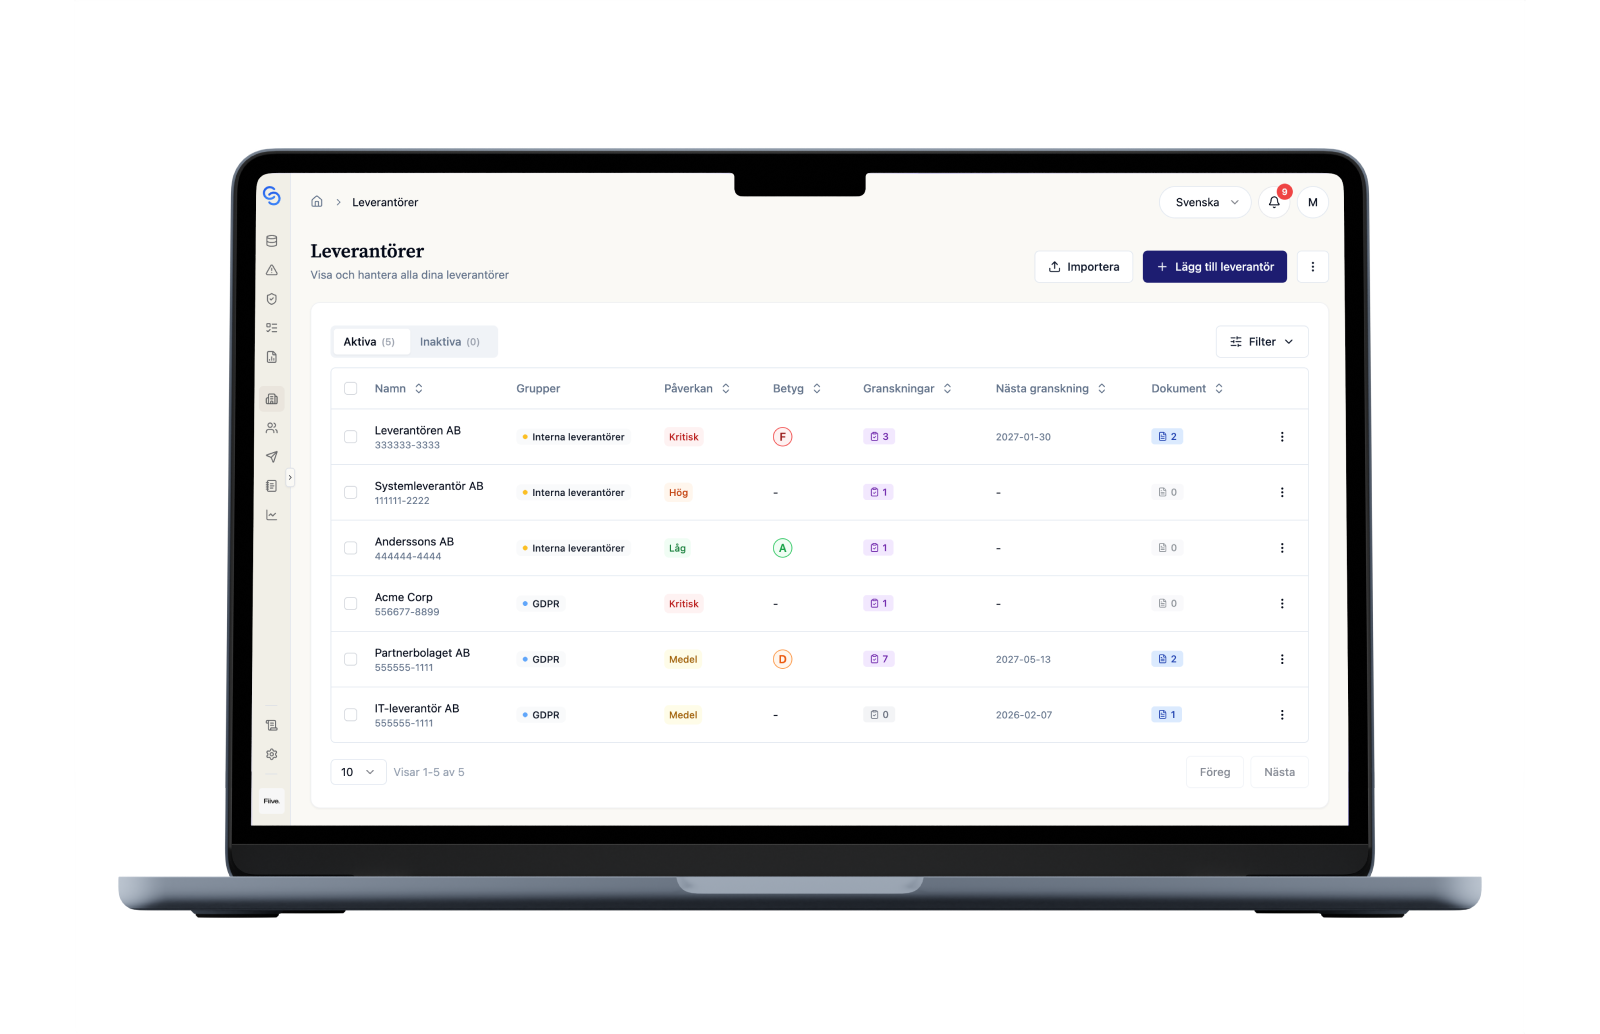
ChainSec is a Swedish system for supplier evaluation and GRC. See which suppliers are approved, which certificates are valid and when reassessments are due.
For teams responsible for security, risks and requirements. Manage internal risks, work with NIS2 requirements and track actions with owners and status.
Import your list via CSV. Add contacts and classify your suppliers.
Assess and document
Collect questionnaire responses, review evidence and document approvals with a history.
Follow up over time
See certificate expiry dates and when suppliers are due for reassessment. Record complaints and nonconformities, assign actions and verify that they have been resolved.
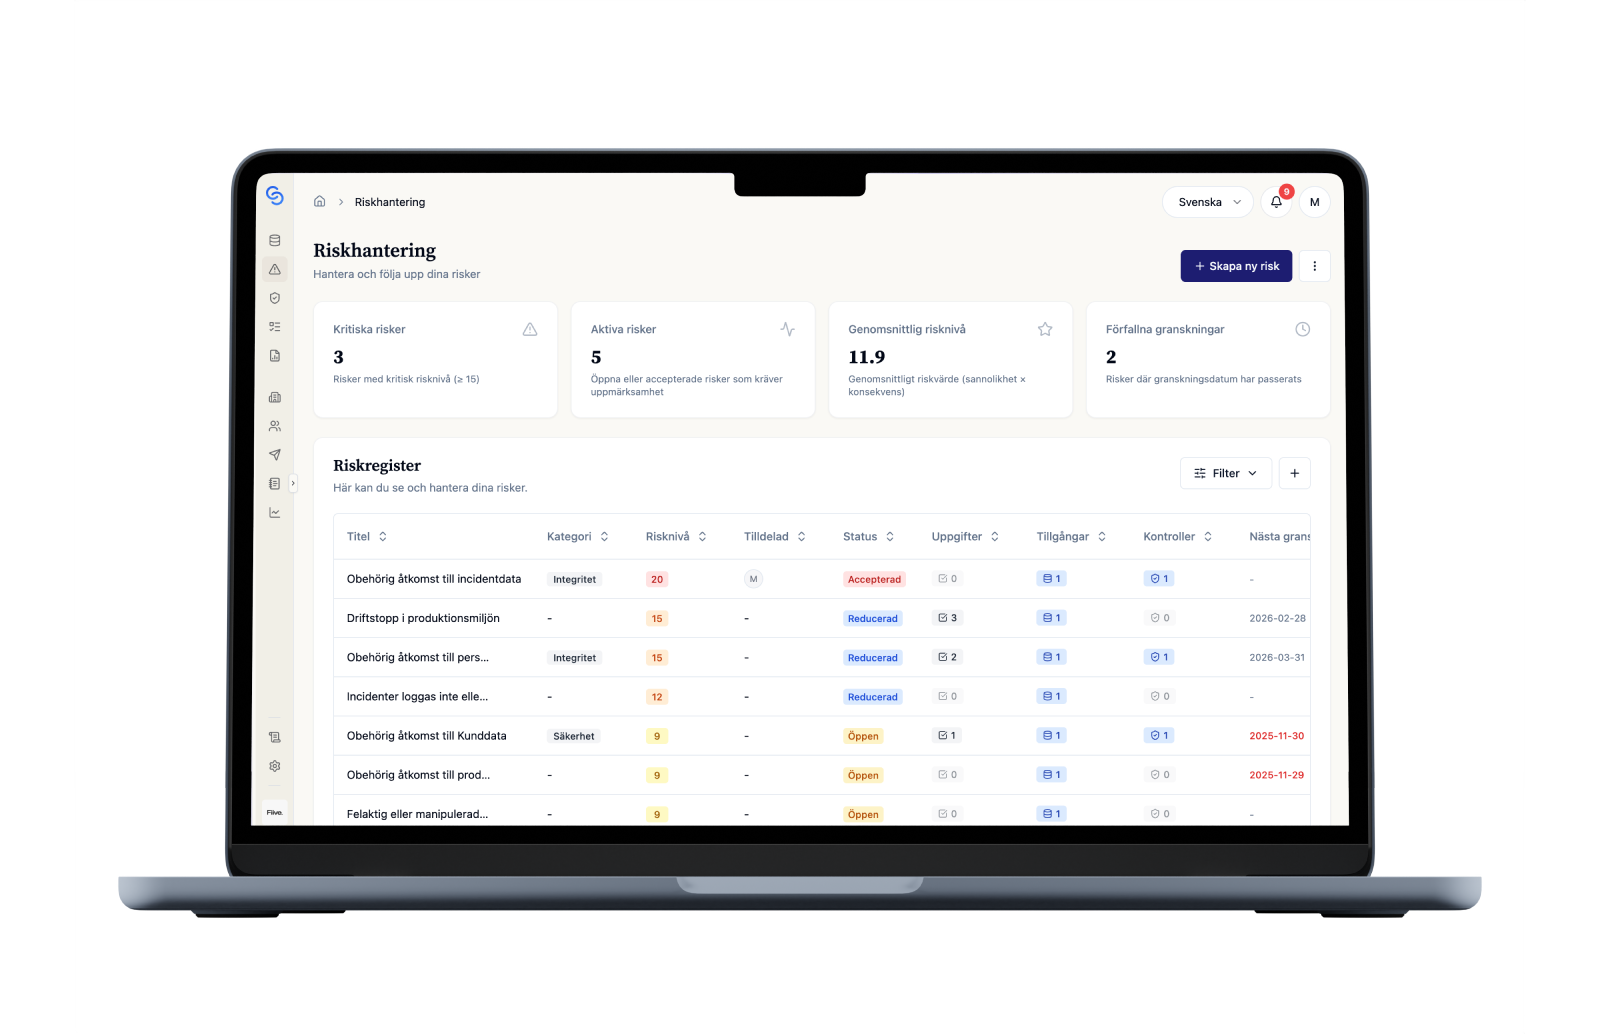
Risk management in ChainSec. Sample data.
For security teams
Give every risk a next step.
Assess supplier security, keep internal risks together and work with NIS2 requirements. Connect gaps to actions with owners and status.
Start with the list you have. Export your spreadsheet to CSV and import the suppliers into ChainSec. Keep statuses, certificates with expiry dates and review history together.
Does it work alongside our management system?
ChainSec keeps suppliers, assessments and evidence organised. Your existing management system continues to handle business processes and document control.
We already have a template from our auditor. What does ChainSec add?
The template helps with the assessment itself. ChainSec also keeps approval status, certificate expiry dates, nonconformities and previous review history together, so you can follow up on the same supplier over time.
How do we manage supplier nonconformities?
Record complaints or audit findings against the supplier. Assign an owner and an action, document the supplier’s response and verify that the nonconformity is resolved before closing it. The history is retained.
Can we also work with internal risks and requirements?
Yes. Supplier follow-up covers quality and environmental practices. With GRC, you also work with supplier security assessments, internal risks, requirements and actions. Add Data Protection when needed.
See how it could work for you.
We start with your work and show you the part of ChainSec that is relevant to your team.