GDPR · ChainSec GRC
Bring data protection together.
Follow up the evidence.
Keep processors, processing activities and risks organized. Gather the documentation and follow up security measures in your data protection work.
What does GDPR entail?
The General Data Protection Regulation (GDPR) is the EU's legislation for the protection of personal data that came into force in 2018. The regulation gives individuals control over their personal data and places high demands on organizations that process this type of information.
- Data processors
- Keep track of who processes personal data on your behalf.
- Risk-based measures
- Assess risks to individuals and document appropriate protective measures.
- Accountability
- Be able to demonstrate how you apply the principles for processing personal data.
From requirements to work
Keep shared records of your data protection work.
ChainSec supports documentation of processors, risks and security measures. The Article 30 register is available in Data protection, added on top of Risk and requirements. You remain responsible for the legal assessment of processing activities.
| Work area | Support in ChainSec | Evidence to follow up |
|---|---|---|
| Security measures · Article 32 | Document your own controls and security measures. Identify gaps, create actions and follow up implementation. A pre-built GDPR catalog is planned. | Documented controls and linked actions. |
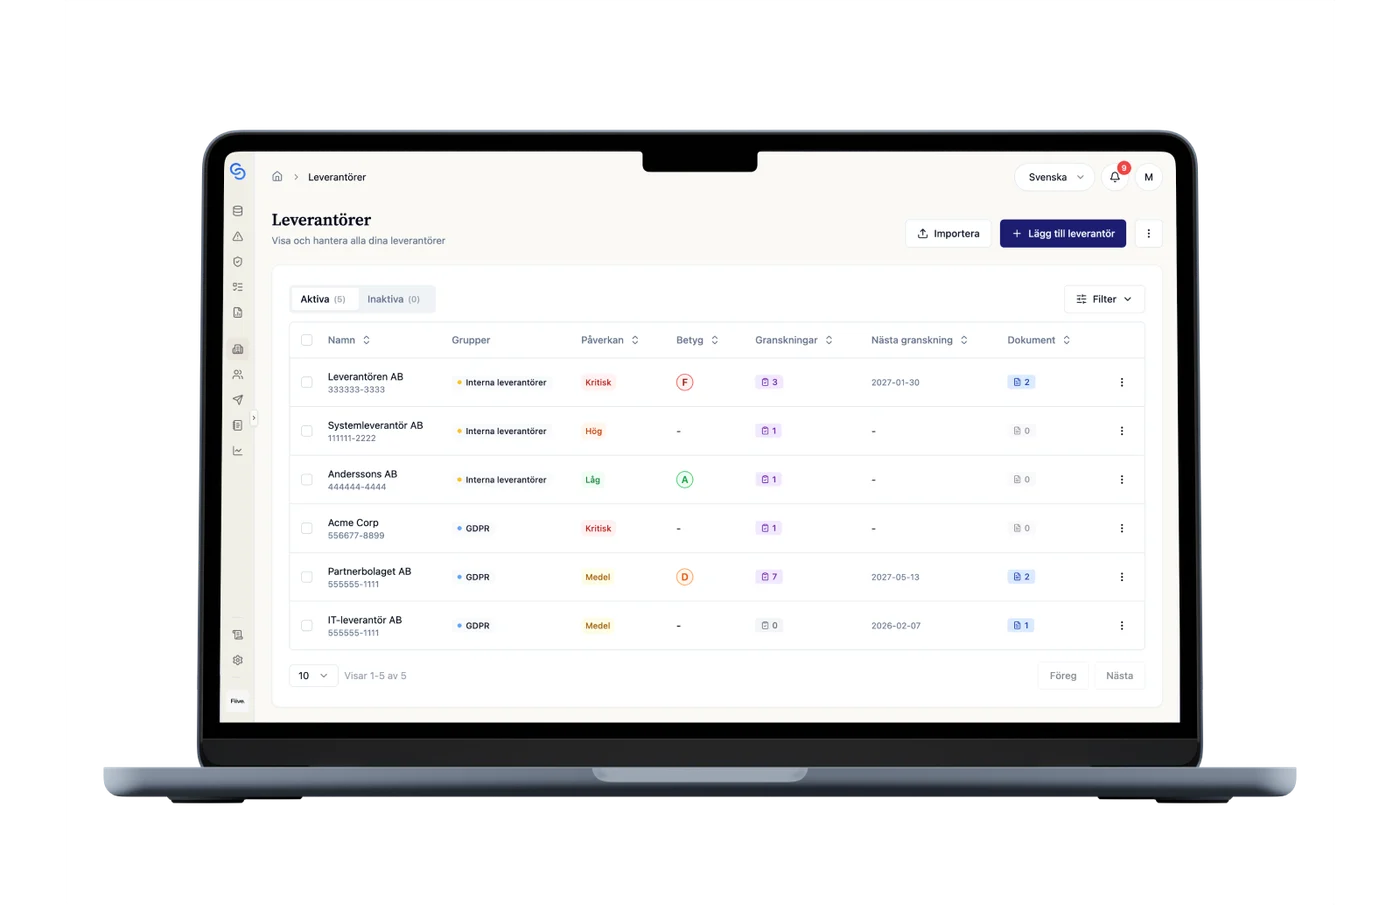
| Data processors · Article 28 | GDPR Article 28 requires verified processor controls. Register processors in the supplier registry and send data protection assessments — built-in DPA tracking is on the roadmap. | Supplier register, documents and assessment history. |
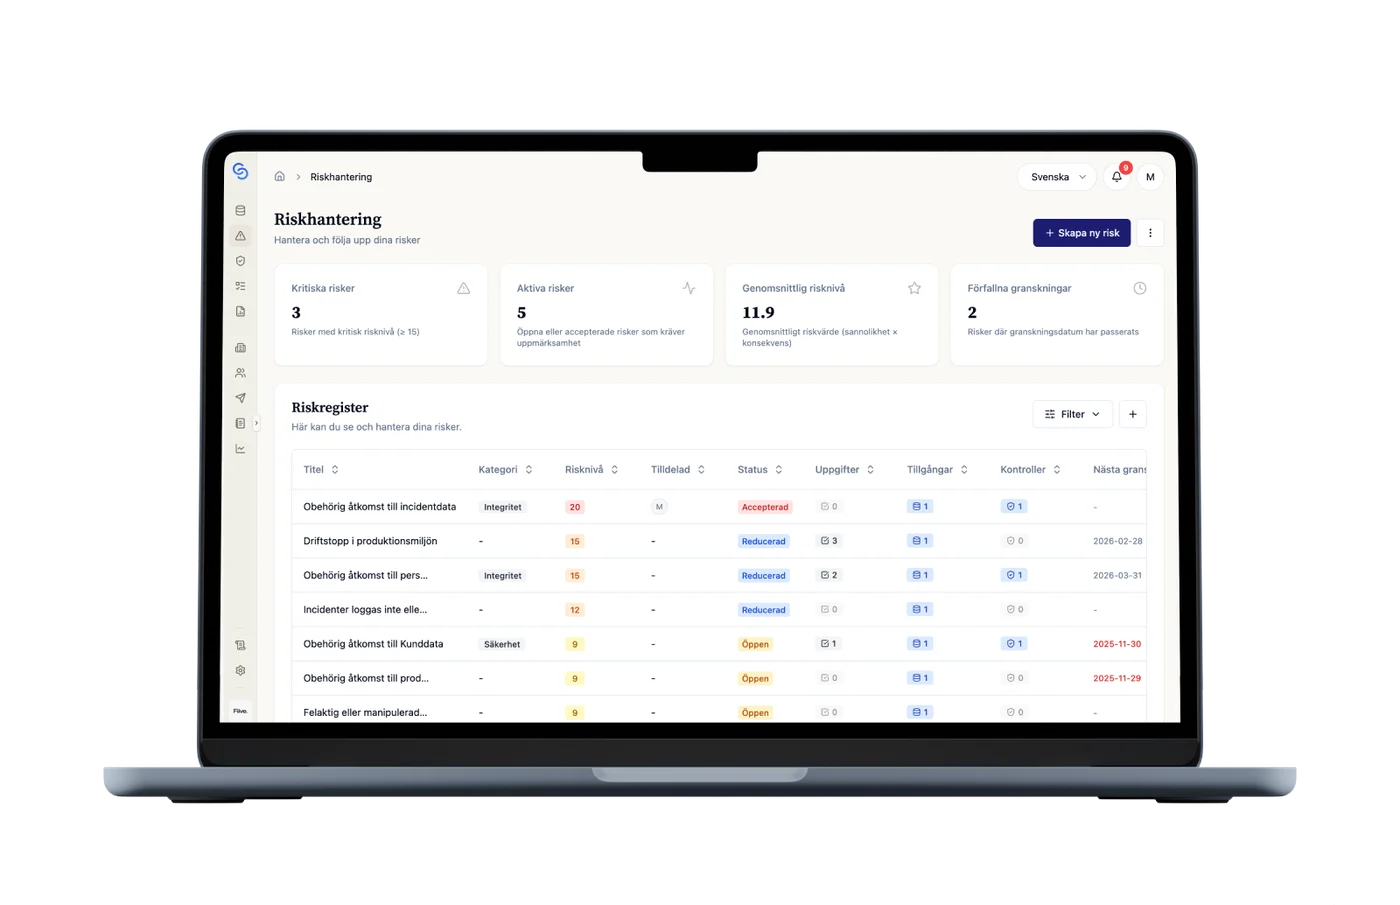
| Risk evidence for DPIA · Article 35 | GDPR Article 35 requires assessments for high-risk processing. Use the risk register to document high-risk processing assessments, assess risks to data subjects and link protective measures. | Risk assessments and selected protective measures. |
| Documentation · Articles 5(2) and 30 | Gather documentation of security measures, processor reviews and risks. Keep processing activities in the Article 30 register in Data protection. | Article 30 register and documented security work. |
In your daily work
From documentation to regular follow-up.
Keep supplier reviews, risks and actions connected in your daily work.
Control management for GDPR requirements
Document your own controls and security measures. Identify gaps, create actions and follow up implementation. A pre-built GDPR catalog is planned.
Supplier registry for data processors
Document processors in the supplier register, upload supporting documents and send assessments. Dedicated DPA tracking is planned.
Risk management for DPIA
GDPR requires Data Protection Impact Assessments (DPIA) for high-risk processing. Document processing activities, assess risks to data subjects in the risk matrix, and link protective measures to minimize risks.
Questions about GDPR
What is GDPR?
GDPR (General Data Protection Regulation) is the EU's legislation for the protection of personal data that came into force on May 25, 2018. The regulation regulates how organizations may collect, use, store, and share personal data and gives individuals strengthened rights regarding their data.
What penalties do we risk for inadequate GDPR compliance?
Penalties for GDPR violations can be substantial - up to 20 million euros or 4% of global annual turnover, depending on which amount is higher. In addition, inadequate compliance can lead to damaged trust with customers and partners, which can have long-term negative effects on the business.
How does GDPR affect the management of suppliers?
When you hire suppliers (data processors) who process personal data on your behalf, you remain ultimately responsible for GDPR compliance. This requires clear data processing agreements, due diligence before hiring, and continuous follow-up of suppliers' data protection work. You must verify that your suppliers have appropriate technical and organizational security measures in place.
What is a Data Protection Impact Assessment (DPIA) and when is it needed?
A Data Protection Impact Assessment (DPIA) is a process to identify and minimize risks with personal data processing. It is required under GDPR when processing is likely to result in high risk to individuals' rights and freedoms, particularly when using new technology, systematic monitoring, or processing sensitive personal data on a large scale.
How can ChainSec help us with GDPR compliance?
ChainSec supports documentation of data processors, processing activities, risks and security measures. Data protection includes an Article 30 register and asset classification. You document your own controls; a pre-built GDPR catalog and built-in DPA tracking are planned. ChainSec provides evidence for your work, while legal assessments remain your responsibility.
How does GDPR relate to other regulations such as ISO 27001 and NIS2?
GDPR focuses specifically on the protection of personal data, while ISO 27001 is a broader standard for information security and NIS2 focuses on cybersecurity in critical sectors. There are significant overlaps between the regulations, particularly around risk management and security measures. By using ChainSec, you can consolidate your work with all these regulations in a common platform and benefit from synergies between them.
See your GDPR work in ChainSec.
We show the risks, requirements and follow-up based on how you work today. After the demo, you can try ChainSec for free.