NIS2 · ChainSec GRC
NIS2 software for your team.
Keep work and evidence together.
For small and medium-sized businesses managing NIS2 work. Bring supplier assessments, risks and requirements together in ChainSec and link gaps to owners and actions.
What does the Cybersecurity Act (NIS2) entail?
The Cybersecurity Act is Sweden's implementation of the EU's NIS2 directive and took effect on January 15, 2026. The law applies to both public and private actors in critical sectors and aims to raise cybersecurity throughout the EU through harmonized requirements.
- Supply chain security
- Assess suppliers, document security requirements and follow up gaps.
- Systematic security work
- Document controls, ownership and how security work is followed up.
- Risks and actions
- Use risk assessments to prioritize the measures you need to implement.
From requirements to work
Connect requirements to the work.
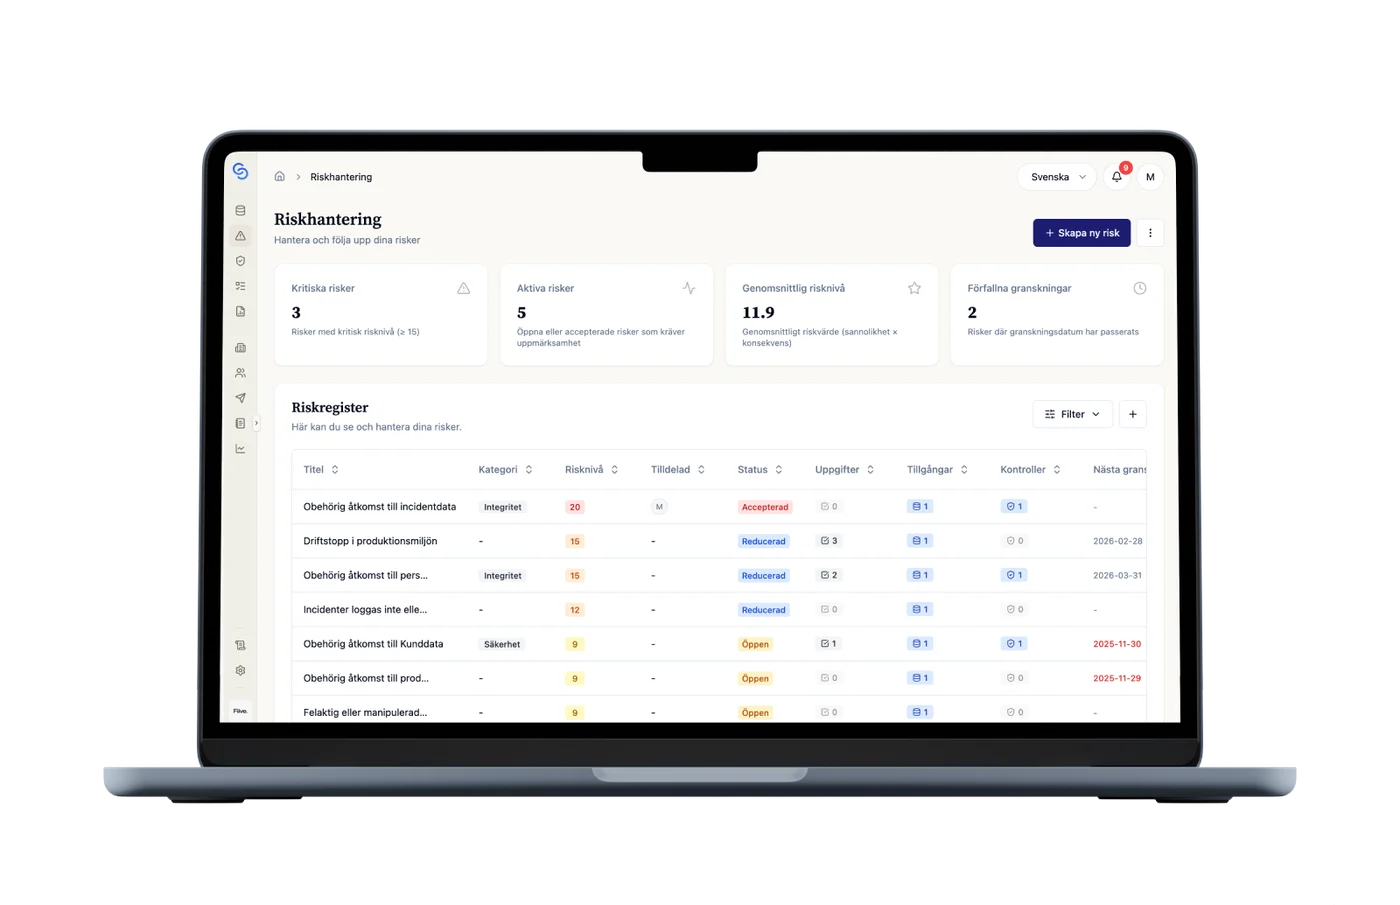
The Cybersecurity Act requires structure around suppliers, risks and controls. ChainSec brings supplier assessments, risks, requirements and actions together in one system, so you can see who is responsible and what remains.
| Work area | Support in ChainSec | Evidence to follow up |
|---|---|---|
| Supply chain | Gather all suppliers in one register with classification, certificates and review history, and send security assessments directly from ChainSec. | Supplier register, assessments and review history. |
| NIS2 requirements and gaps | Use the NIS2 requirements catalogue to assess your current position. Record gaps and create actions with an owner, deadline and status, then follow up on what remains. | Requirement status, owners and linked actions. |
| Risk management | Register assets in the asset register, assess ICT risks in the risk matrix and link security controls to each risk. Show supervisory authorities that your security priorities follow actual risk — not guesswork. | Assets, risk assessments and risk treatment. |
| Documentation and follow-up | Gather supplier assessments, risk records, control status and actions. Use the records when compiling documentation for supervision. | Supporting records of suppliers, risks and actions. |
In your daily work
From documentation to regular follow-up.
Keep supplier reviews, risks and actions connected in your daily work.
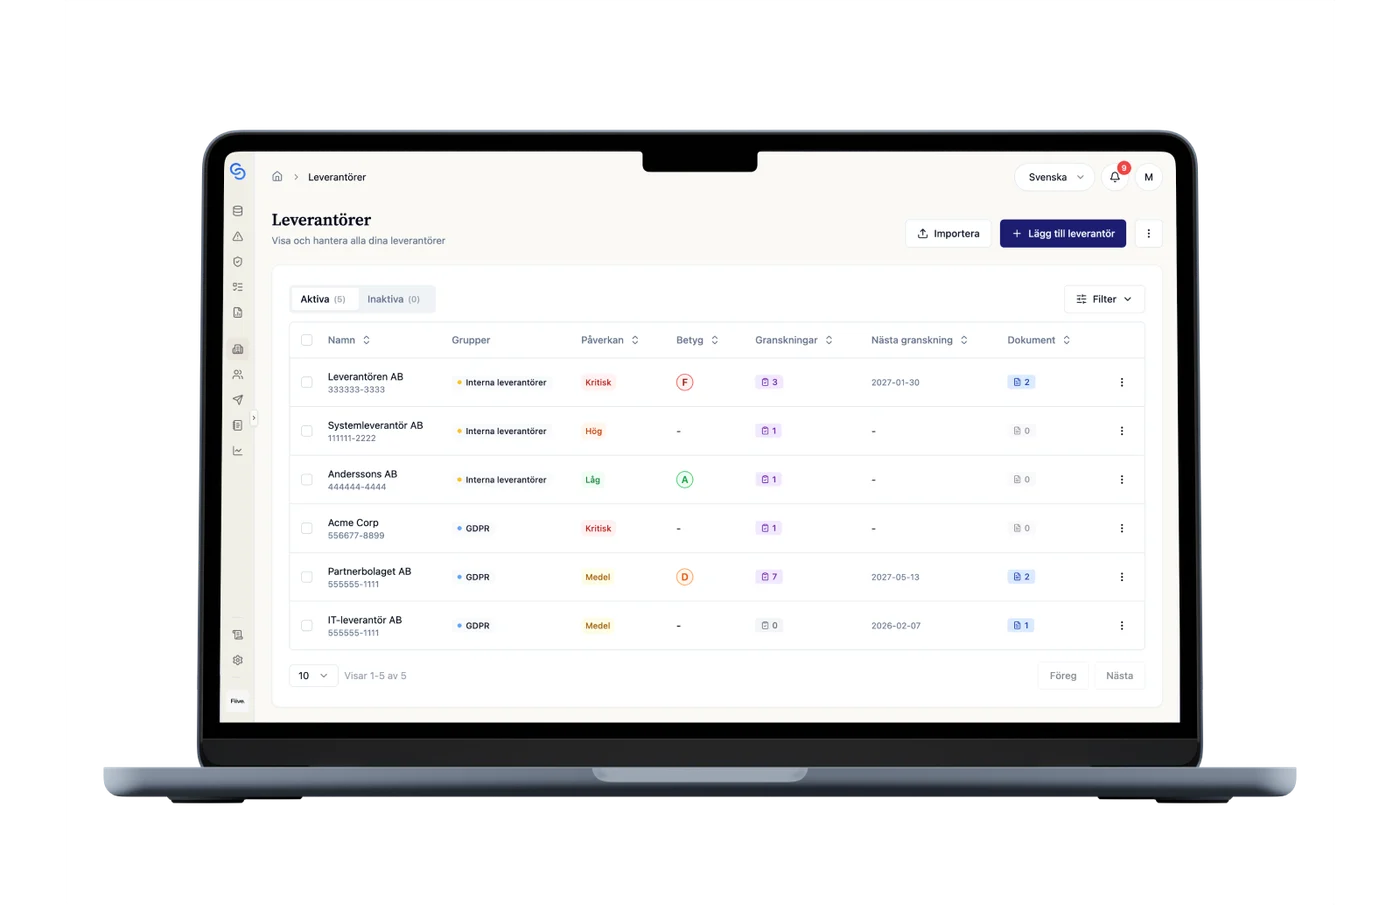
One place for all suppliers
Gather all suppliers in one register, follow up certificates and reviews, and send out security assessments directly — without switching tools.
See which requirements need work
Assess your current position with the NIS2 requirements catalogue. Document gaps, create actions with an owner and deadline, and follow up what remains.
Risks and controls stay connected
Document information assets, assess ICT risks and link controls to them. You avoid keeping the risk register in one document and the controls in another.
Read more
Questions about NIS2
What is the Cybersecurity Act (NIS2)?
The Cybersecurity Act is Sweden's implementation of the EU's NIS2 directive. The law took effect on January 15, 2026, and means that organizations in critical sectors must work more systematically with information and supplier security. Requirements include risk management, technical and organizational protective measures, incident reporting, and documentation.
When does NIS2 take effect in Sweden?
The law took effect on January 15, 2026. NIS2 was supposed to be implemented in 2024 but was delayed. Now that the law is in force, supervisory authorities can begin reviewing organizations — it is high time to have documentation and processes in place.
Which organizations are covered by NIS2?
NIS2 applies to medium-sized and large organizations in 18 critical sectors – including energy, transport, digital infrastructure, banking, healthcare, water, manufacturing, and food. Certain digital service providers and suppliers to critical organizations are also covered.
What requirements does NIS2 place on organizations?
Core requirements are systematic security work, risk-based measures, protection of critical systems, continuity management, incident reporting with an early warning within 24 hours, incident notification within 72 hours and a final report within one month, and documentation of both risks and measures. The law also requires that management must be involved and trained in cybersecurity.
What does supplier responsibility mean in NIS2?
Organizations must ensure that their suppliers maintain a sufficient security level. This includes risk assessments, requirement setting in contracts, security assessments, and regular follow-up. The supply chain is just as important as internal security.
What penalties can you get for lack of compliance?
Essential entities can receive a penalty fee of up to the higher of 10 million euros and 2% of global turnover. For important entities the cap is the higher of 7 million euros and 1.4%. In serious cases, management personnel may be prohibited from exercising management assignments.
What is the difference between essential and important entities?
Classification is determined by a combination of sector and size. Large organizations (250 or more employees, or turnover above 50 million euros and a balance sheet total above 43 million euros) in highly critical sectors such as energy, transport, banking and healthcare are classified as essential and receive proactive supervision. Medium-sized organizations in the same sectors, and organizations in the other NIS2 sectors, are classified as important and are primarily reviewed in case of complaints, incidents or suspected deficiencies. Certain types of entities are always essential regardless of size.
How does ChainSec help organizations meet NIS2?
ChainSec supports supplier assessments, the NIS2 requirements catalogue, risk management and linked actions. Suppliers, assets, risks and follow-up are documented in one place. You are responsible for assessing and meeting the requirements.
See your NIS2 work in ChainSec.
We show the risks, requirements and follow-up based on how you work today. After the demo, you can try ChainSec for free.