DORA · ChainSec GRC
Bring ICT suppliers together.
Keep risks in view.
Document ICT providers, link risks to assets and follow up security assessments. Shared records for the parts of your DORA work that ChainSec supports.
What is DORA and who is covered?
The Digital Operational Resilience Act (DORA) is an EU regulation that applies from 17 January 2025 (it entered into force in January 2023) and aims to strengthen digital resilience within the financial sector. The regulation covers banks, insurance companies, investment firms, payment institutions, pension institutions, and other financial actors, as well as their critical ICT service providers.
- Digital resilience
- DORA applies to financial entities and brings together requirements for digital operational resilience.
- ICT third-party risks
- Identify dependencies on ICT providers and assess the risks they introduce.
- Documented follow-up
- Document assessments and follow up risk management and measures.
From requirements to work
Structure for ICT risks and supplier follow-up.
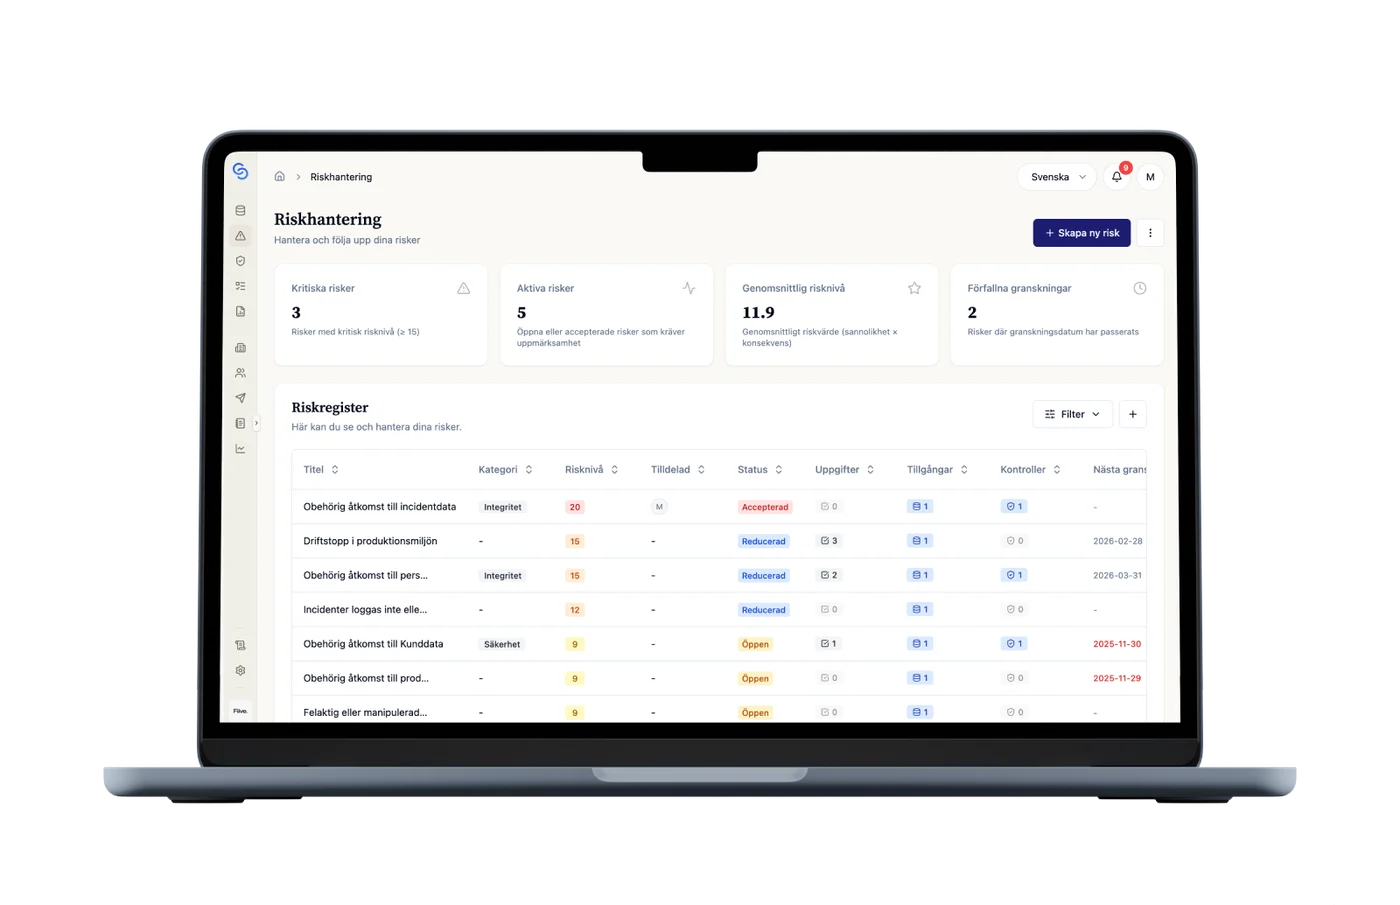
ChainSec is a general GRC tool, not a DORA-specific implementation. Its supplier register, risk register and assessments support parts of the work. You remain responsible for the full DORA register of information, reporting and other requirements.
| Work area | Support in ChainSec | Evidence to follow up |
|---|---|---|
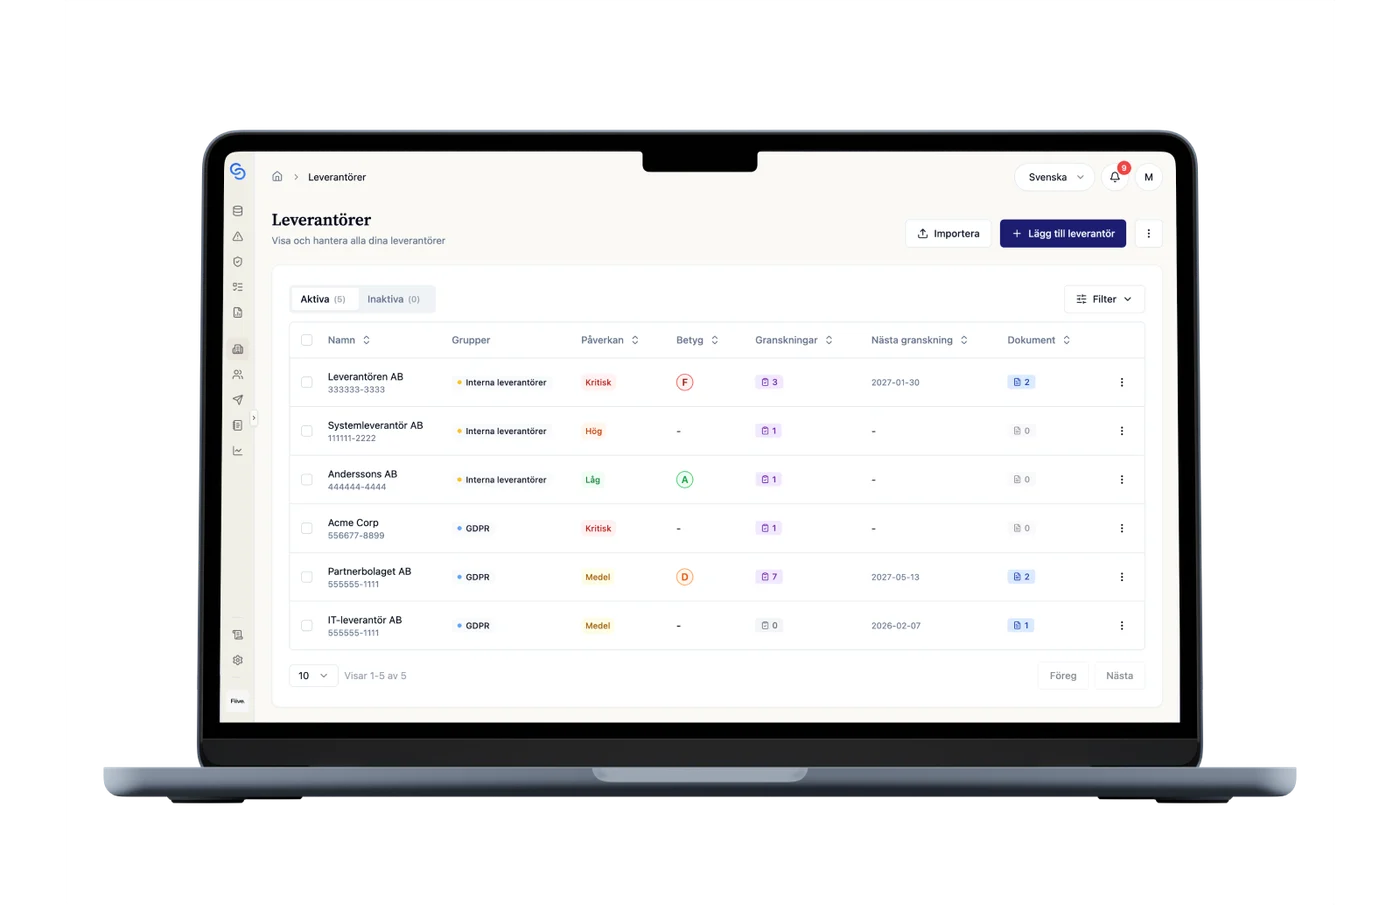
| ICT providers | Gather ICT suppliers in the supplier register, classify them and upload supporting documents. Use the register as a working record alongside your DORA register of information. | Suppliers with classification, documents and contacts. |
| ICT risks and assets | DORA requires a documented ICT risk management framework. Register ICT assets, assess risks in the risk matrix and link security controls to each risk — so your ICT risk management is structured, not ad hoc. | Assets, risk matrix and linked controls. |
| Supplier assessments | DORA requires regular assessment of critical ICT providers. Send structured security assessments that cover resilience, recovery capability and security level. All assessments are documented with full history. | Security assessments and documented follow-up. |
| History and records | Reviews are logged per supplier, and risks and actions are followed up in the same system. Use the history and the approved supplier list export (status, classification, latest review and certificate validity) as input ahead of a review. | Review history, risks and actions. |
In your daily work
From documentation to regular follow-up.
Keep supplier reviews, risks and actions connected in your daily work.
Supplier registry for ICT service providers
Gather ICT suppliers in the supplier register, classify them and upload supporting documents. Use the register as a working record alongside your DORA register of information.
Risk management for ICT risks
DORA requires a documented ICT risk management framework. Document ICT assets in the asset registry, assess ICT risks in the risk matrix, and link security measures to manage risks systematically.
Supplier assessments and monitoring
DORA requires regular assessment of critical ICT providers. Send security assessments to critical providers, track performance, and document continuous monitoring.
Records in one place
Reviews are logged per supplier, and risks and actions are followed up in the same system. The records are in one place instead of in email threads and with different people.
Questions about DORA
When does DORA take effect and who is covered?
DORA applies from 17 January 2025 (the regulation entered into force in January 2023). It covers the financial entities listed in Article 2: banks, insurance companies, investment firms, payment institutions, fund managers, pension institutions and crypto-asset service providers. DORA has proportionality rules and simplified requirements for, among others, microenterprises, and some entities are exempt under Article 2. Check Article 2 for your type of business.
What must we include in our ICT provider register?
You must document all ICT providers with: provider name and contact details, which services they provide, whether they are critical or not, contract information and contract periods, and location where data is stored and processed. The register must be continuously updated.
How do we classify critical ICT providers?
An ICT provider is critical if: the service is difficult to replace in the short term, disruption would significantly impact operations, the provider handles sensitive or business-critical data, or you have significant dependency on the provider. Document the classification and risk assessment.
What clauses are required in ICT provider contracts?
Contracts must include: right to audit the provider's security and processes, requirements for incident reporting to you, documented exit strategies and transition plans, security requirements and SLAs, and information about any sub-processors.
How often should we assess our ICT providers?
DORA sets no fixed interval. Assessments must be carried out regularly and in proportion to how critical the provider is. Conduct security assessments, review their incident management and recovery capability, verify that contract requirements are met, and document all assessments and identified risks.
What is an exit strategy and why is it required?
An exit strategy describes how you can terminate cooperation with an ICT provider without disrupting operations. It should include: alternative providers, transition timeline, how data is transferred, and how continuity is ensured during the switch. This is mandatory for critical providers.
Must we report provider incidents?
Yes, if an ICT provider has an incident that affects your operations, you must report according to DORA's timelines: initial notification within 4 hours of classifying the incident as major and no later than 24 hours after becoming aware of it, an intermediate report within 72 hours of the initial notification, and a final report no later than one month after the latest intermediate report. Also document minor incidents for annual reporting.
How does ChainSec help with DORA provider requirements?
ChainSec is a general GRC tool, not a DORA-specific implementation. Its supplier register, risk register and assessments support parts of the work. You remain responsible for the full DORA register of information, reporting and other requirements.
See your DORA work in ChainSec.
We show the risks, requirements and follow-up based on how you work today. After the demo, you can try ChainSec for free.