ISO 27001 · ChainSec GRC
Bring security work together.
Support your ISMS.
Keep risks, assets, supplier assessments and actions connected. ChainSec supports parts of your ISO 27001 work with shared records to follow up.
What does ISO 27001 entail?
ISO 27001 is an international standard for information security that helps organizations implement, monitor, and continuously improve an Information Security Management System (ISMS). The latest version, ISO/IEC 27001:2022, has 93 controls grouped into four themes (organizational, people, physical and technological controls) in Annex A.
- A systematic ISMS
- The standard defines how information security is managed, documented and reviewed.
- Risk-based decisions
- Assess risks and select the controls relevant to your organization.
- Continuous improvement
- Review security objectives and document improvements over time.
From requirements to work
Evidence for your ISO 27001 work.
ChainSec is not an ISO system and does not replace your management system. We solve certain parts: risks, requirements, suppliers and actions.
| Work area | Support in ChainSec | Evidence to follow up |
|---|---|---|
| Controls and applicability | Document implementation of controls, upload evidence and link policies. Note applicability per control as input to your Statement of Applicability. | Documented implementation and evidence per control. |
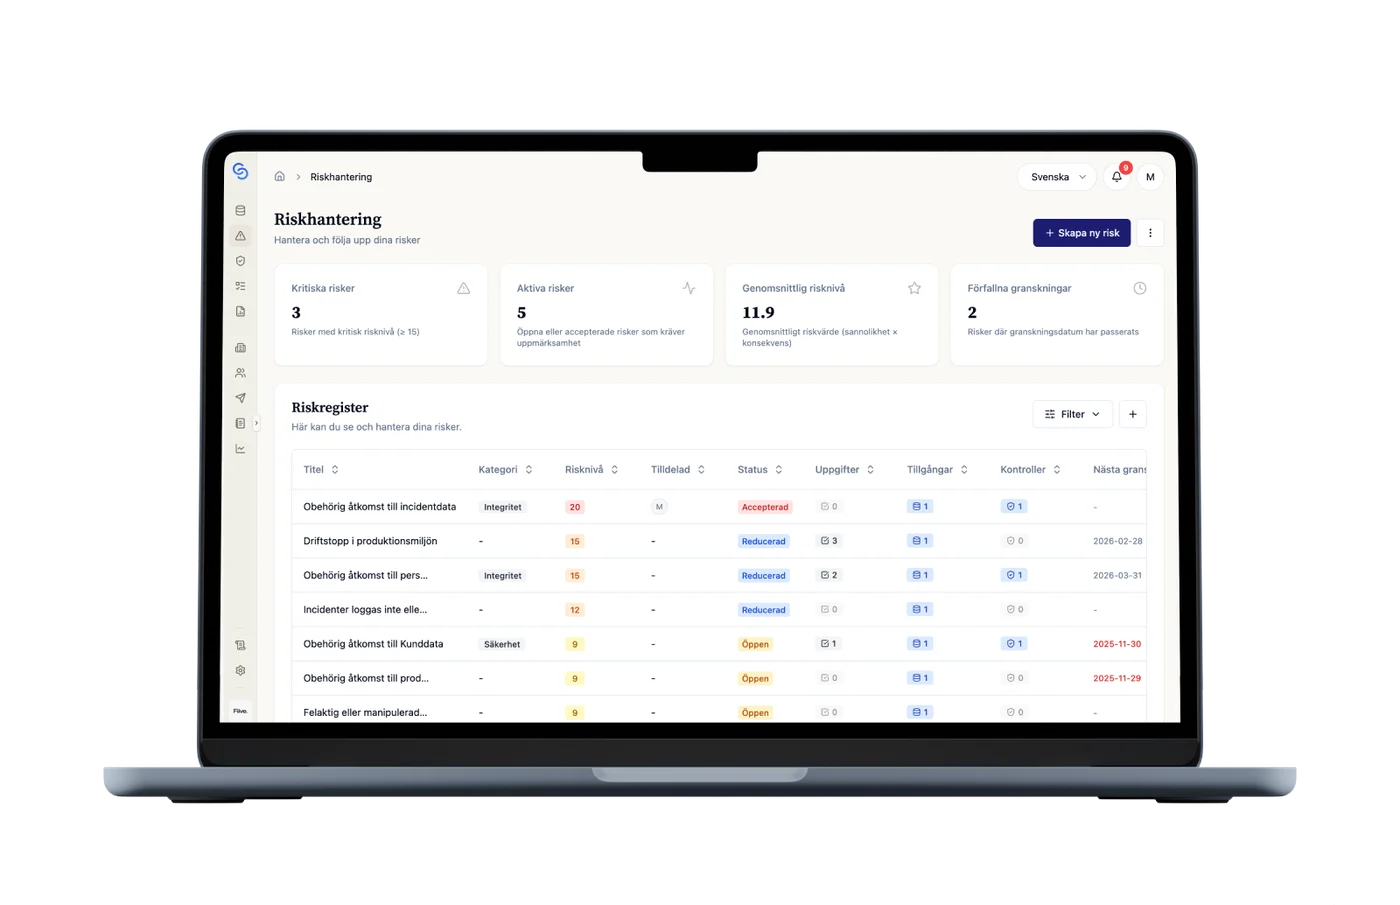
| Risk assessment | Register information assets in the asset register and assess ICT risks in the risk matrix using likelihood × consequence methodology. Link Annex A controls to each risk to show a documented, risk-based approach. | Assets, risk matrix and selected protective measures. |
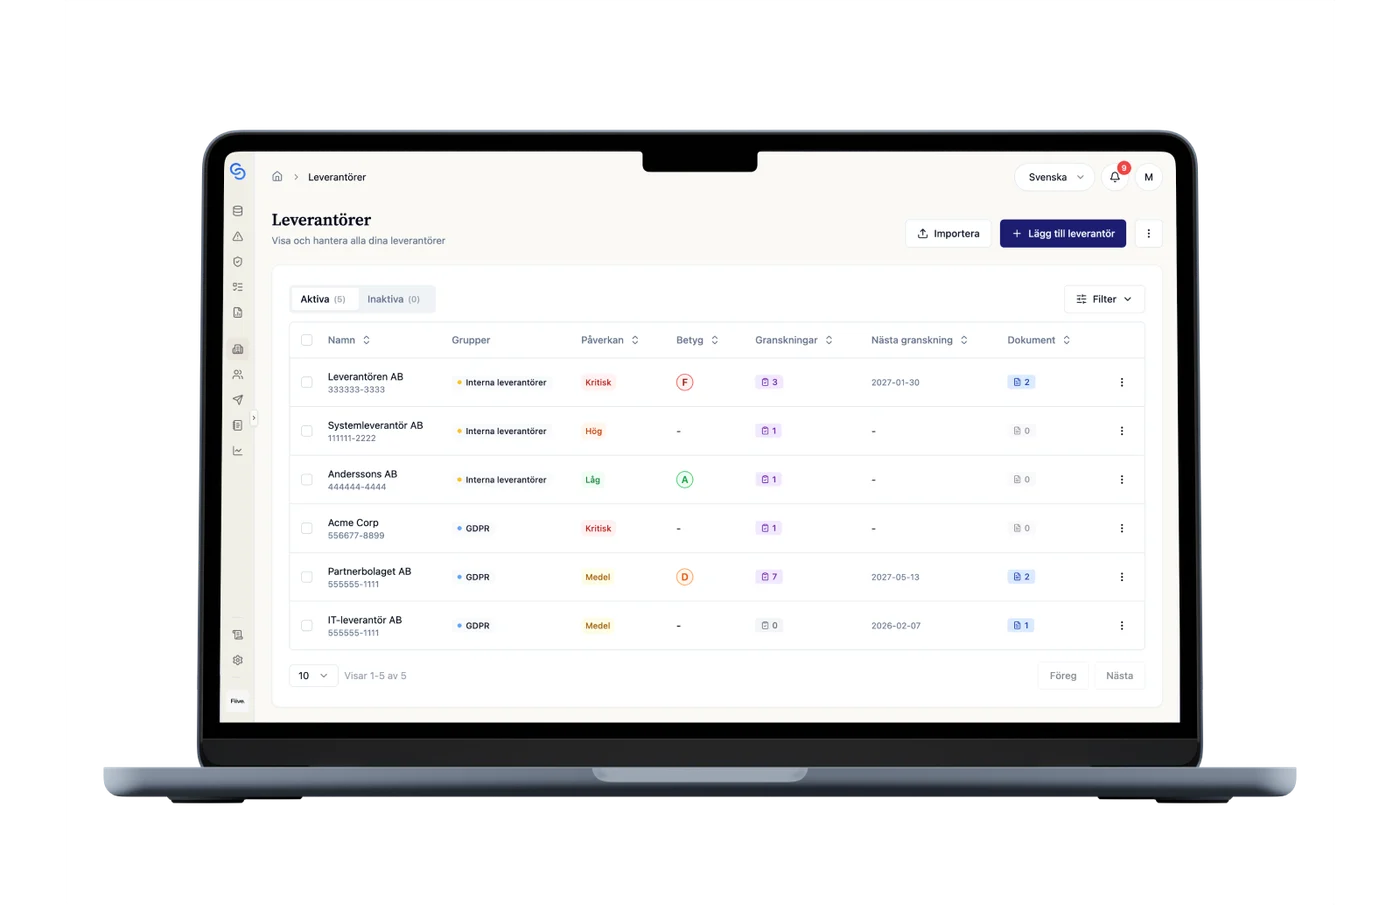
| Supplier security | ISO 27001 Annex A requires documented supplier controls. Gather suppliers in the registry, upload evidence and certificates, send security assessments and track follow-up — structured evidence of how you manage third-party security. | Supplier assessments, certificates and history. |
| Actions and improvement | Create actions for gaps identified in your control work. Assign owners, set deadlines and follow progress. Document the outcome so you can build on the work at the next review. | Owners, deadlines and action status. |
In your daily work
From documentation to regular follow-up.
Keep supplier reviews, risks and actions connected in your daily work.
Controls and evidence for Annex A
Document your own controls, their applicability, implementation and evidence.
Assess risks and follow up treatment
Assess risks using likelihood and impact. Document how risks will be treated and link them to requirements and actions. With the Data protection add-on, you can also document assets and link them to risks.
Supplier security according to A.5.19-A.5.23
Document suppliers, send security assessments and follow up the evidence for supplier controls in A.5.19–A.5.23.
Questions about ISO 27001
What is ISO 27001?
ISO 27001 is an international standard for Information Security Management Systems (ISMS) that provides a systematic approach to managing sensitive company information. The standard contains requirements for how organizations should establish, implement, maintain, and continuously improve their information security work.
How does ChainSec help with ISO 27001 compliance?
ChainSec supports risk management, an asset register, supplier security assessments, controls and actions. You document your own controls and evidence. ChainSec does not replace your ISMS or the work required for certification.
What are the benefits of ISO 27001 certification?
An ISO 27001 certification provides many benefits, including improved security management, increased credibility with customers and partners, better compliance with laws and regulations, reduced risk of security incidents, and potential cost savings through more efficient processes.
How long does it take to get started with ChainSec?
Start by importing your suppliers via CSV, adding assets and documenting risks. We show the workflow in a demo, after which you can try the platform for free.
How does ISO 27001 relate to supplier security?
ISO 27001 sets specific requirements for managing supplier relationships in controls A.5.19–A.5.23 (in the 2022 version, previously A.15 in the 2013 version). Organizations must verify that suppliers with access to sensitive information follow appropriate security procedures. This includes risk assessments of suppliers, security agreements, and continuous monitoring of suppliers' security work. ChainSec supports this with ready-made supplier security assessments and a central registry.
See your ISO 27001 work in ChainSec.
We show the risks, requirements and follow-up based on how you work today. After the demo, you can try ChainSec for free.