ISO 9001 · ChainSec Supplier
Keep suppliers in order.
Evidence for clause 8.4.
ISO 9001:2015 clause 8.4 requires companies to evaluate, select, monitor and re-evaluate their external providers against documented criteria and to show the evidence at audit. ChainSec is a supplier register for quality and environment managers that keeps the approved supplier list, certificates, re-evaluation and nonconformities in order — not a management system.
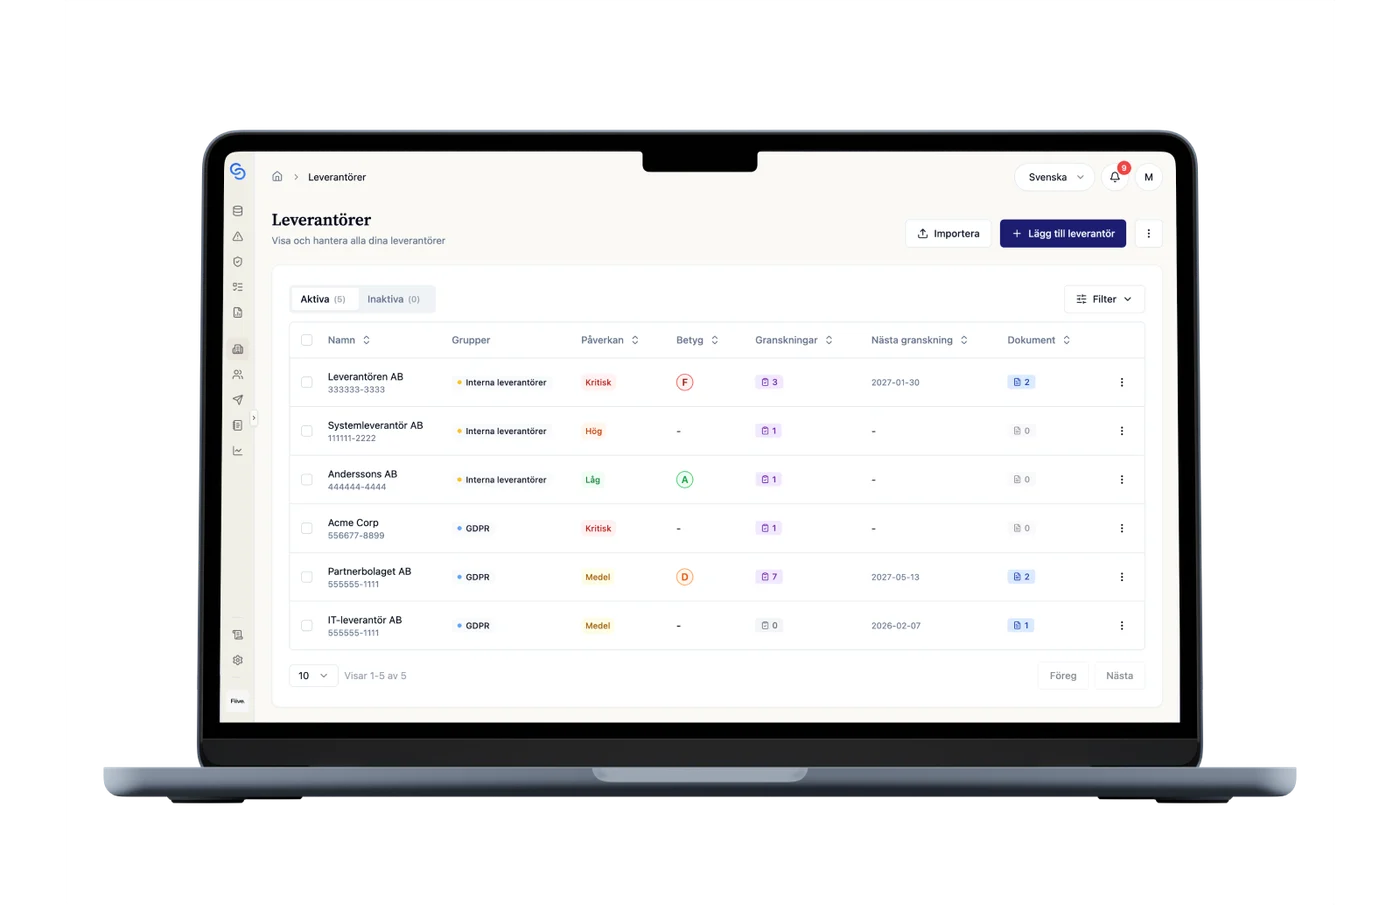
From requirements to work
Is ChainSec an ISO 9001 system?
No. ChainSec does not replace your management system. It supports supplier evaluation, classification, certificates, re-evaluation and supplier nonconformities — the work your auditor asks about in clause 8.4.
| Clause | What ISO 9001 requires | Where it is done and what the auditor wants to see |
|---|---|---|
| 8.4.1 | Criteria for the evaluation, selection, monitoring and re-evaluation of external providers, and documented information on each step. | ChainSec — approval status, review log and export of the approved supplier list. The auditor wants to see the criteria and that each supplier was evaluated against them. |
| 8.4.2 | Controls proportionate to how much the provider affects your ability to meet customer requirements. | ChainSec — classification and re-evaluation interval per supplier. The auditor wants to see that controls differ between critical and other suppliers. |
| 8.4.3 | Requirements communicated to the provider before a contract or purchase order. | Partly — questionnaires and documents in ChainSec, the requirements in your contracts and purchase orders. The auditor wants to see the requirements on the purchase order or in the contract before ordering. |
| 10.2 | Nonconformities handled with action, root cause analysis and a check that the action worked. | ChainSec for supplier nonconformities, your management system for internal ones. The auditor wants to see what happened, which action was taken and that it was verified. |
| 6.1 | Risks and opportunities are identified and addressed. | The Risk and requirements add-on |
| 7.5, 9.2, 9.3 | Document control, internal audit and management review. | Your management system |
What does ISO 9001 clause 8.4 require of suppliers?
Clause 8.4 requires you to evaluate, select, monitor and re-evaluate the external providers that affect your ability to meet customer requirements. The criteria must be documented, the controls must be proportionate to the provider’s impact, and you must be able to show what was done.
An external provider is a broader concept than purchasing. It also covers outsourced processes such as IT operations, calibration and group companies outside the scope of your management system — and the responsibility stays with you even when someone else does the work. The clause numbers on this page follow ISO 9001:2015. ISO 9001:2026 was published on 16 September 2026, so check with your certification body which edition and transition plan apply. The standard is published by ISO.
In your daily work
How do you keep suppliers in order ahead of an audit?
Supplier follow-up is often someone’s job on the side of their real job. These are the steps, in the order most teams take them.
Import your supplier list
Export your spreadsheet to CSV and import it. The spreadsheet is the onboarding, so you keep it. Imported suppliers are approved on arrival, and the history shows they came in through the import.
Classify and set a re-evaluation interval
Classify each supplier by how much it affects your delivery and choose how often it is re-evaluated: every three, six or twelve months. That makes the proportionate control in 8.4.2 visible per supplier.
Evaluate and collect evidence
Send supplier assessments for quality to the critical suppliers. Adapt the questions to your criteria and collect responses and certificates as evidence.
Review and re-evaluate with history
Every review is logged with date, outcome and who did it. Checklists per supplier keep track of the steps that need doing each time.
Export the approved supplier list
An export with status, classification, latest review and certificate validity. It is the first document an auditor or a large customer asks for.
How do you handle nonconformities and complaints against suppliers?
A complaint in an email is not enough at audit. The auditor wants to see what happened, what the supplier answered, which action was taken and who verified that it worked. In ChainSec, the nonconformity belongs to the supplier, and open cases stay in the todo list until closed.
- Record
- What happened, the source — complaint, audit finding or questionnaire answer — severity and who is responsible. The responsible person can be someone in purchasing or production without a ChainSec account.
- Follow up
- Action, root cause and the supplier’s response in one place. A flagged questionnaire answer can become a nonconformity straight from the review.
- Verify and close
- Someone verifies that the action worked, and ChainSec records who and when. Closing an unfounded complaint without verification requires an explanation that is logged separately.
How often should suppliers be re-evaluated under ISO 9001?
ISO 9001 sets no fixed interval. The requirement is that you have criteria for re-evaluation and can show that you follow them. A common approach is yearly re-evaluation of critical suppliers and less often for the rest, plus re-evaluation after events such as a serious nonconformity or a change of ownership.
A missed re-evaluation is a common gap to check before an audit: the company evaluated the supplier at the start and never again. In ChainSec every supplier has its own interval and a history showing when it was last reviewed.
Is Excel, the management system or a consultant’s template enough?
- “We use Excel.”
- Excel is not bad. It just does not tell you when a certificate has expired or a re-evaluation is overdue, and the auditor asks for history the spreadsheet overwrites. You keep the spreadsheet — it becomes the import file.
- “Our management system already does this.”
- Many management systems include a supplier evaluation form. The difference is a supplier register that keeps status, validity and history per supplier. If the complaint already lives in your system, you reference the case and keep the details there.
- “Our consultant gave us a template.”
- The template solves the first evaluation. It does not solve the fourteenth re-evaluation, or the question of who approved what and when.
Questions about ISO 9001
Is ChainSec an ISO 9001 system?
No. ChainSec does not replace your management system and has no document control, process maps or internal audit. ChainSec does the supplier part: supplier register, classification, re-evaluation, certificates, approved supplier list and supplier nonconformities. The Risk and requirements add-on covers internal risks and requirements.
What does ISO 9001 clause 8.4 require of suppliers?
Clause 8.4 requires you to evaluate, select, monitor and re-evaluate external providers that affect your ability to meet customer requirements, with documented criteria and controls proportionate to the provider’s impact. Requirements must be communicated to the provider before a contract or purchase order.
How often should suppliers be re-evaluated under ISO 9001?
The standard sets no fixed interval. Set the interval per supplier based on risk. You decide the criteria and must be able to show that you follow them. A common approach is yearly re-evaluation of critical suppliers and less often for the rest, plus re-evaluation after events such as a serious nonconformity.
What do we show the auditor?
The approved supplier list as an export with status, classification, latest review and certificate validity. Per supplier you have the review history, the certificates and the nonconformities — open and closed, with who verified the action and when.
Can we keep complaints in our ERP or management system?
Yes. A nonconformity in ChainSec can reference the case number in your ERP or management system. The details stay there, and ChainSec keeps the link to the supplier and the follow-up the auditor asks about.
Does ChainSec work for ISO 14001?
Yes. Assess supplier environmental practices with questionnaires and follow up on certificates and nonconformities. Adapt the questions to your environmental requirements and use the responses as evidence within your management system.
See your supplier workflow in ChainSec.
We show the supplier register, certificates and review history using your workflow. After the demo, you can try ChainSec for free.