Assess supplier security
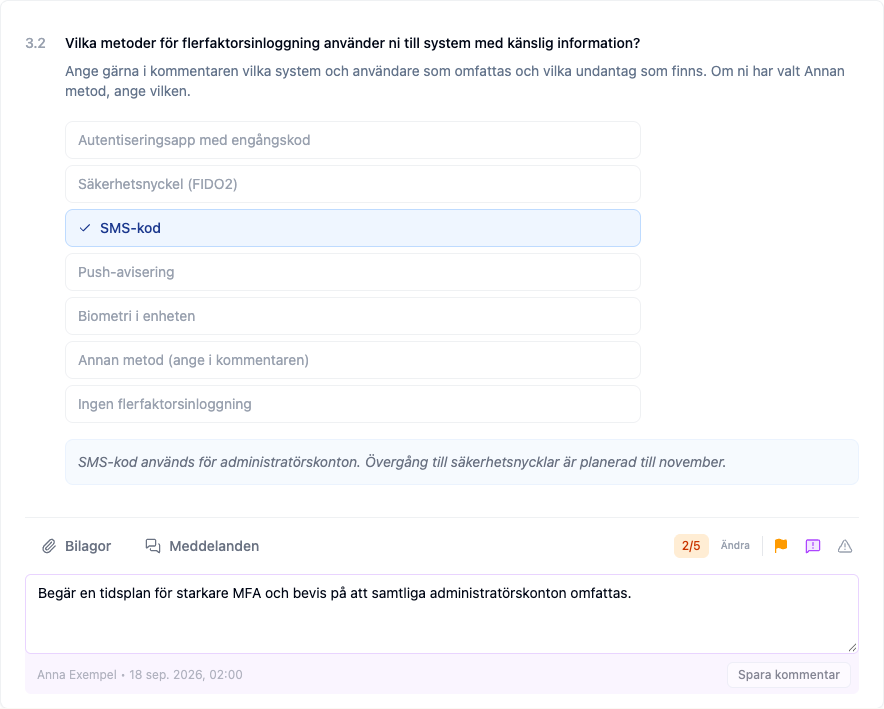
Send security assessments for NIS2 and ISO 27001 at three levels of depth, depending on how critical the supplier is. Flag answers that need follow-up and request evidence directly in the answer.
GRC for security leads
A GRC system for small and medium-sized businesses. Assess supplier security, manage internal risks and work through the NIS2 requirements. Follow up each gap with an owner, an action and a status.
NIS2 counts supply chain security as one of ten areas. Review the supplier’s answers, assess the risks and link them to requirements and actions. Follow up on who owns the work and what remains in the same system.
Send security assessments for NIS2 and ISO 27001 at three levels of depth, depending on how critical the supplier is. Flag answers that need follow-up and request evidence directly in the answer.
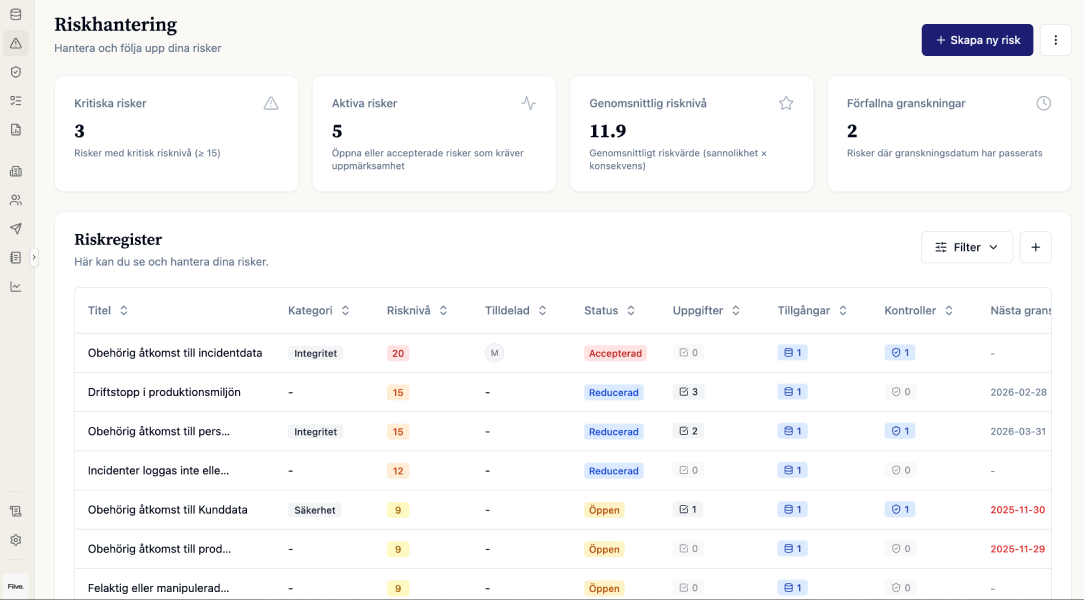
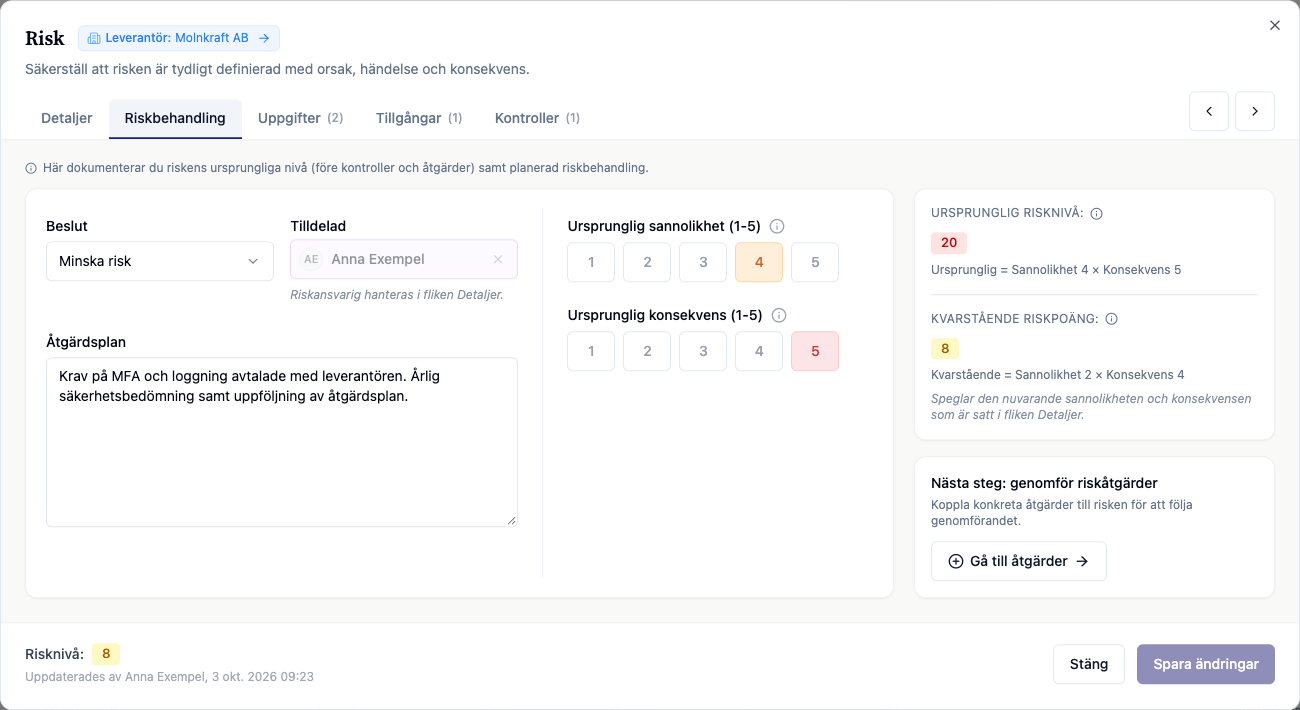
Record the risk in the risk register with likelihood and impact. Decide on treatment, write the action plan and see the residual risk level next to the initial one.
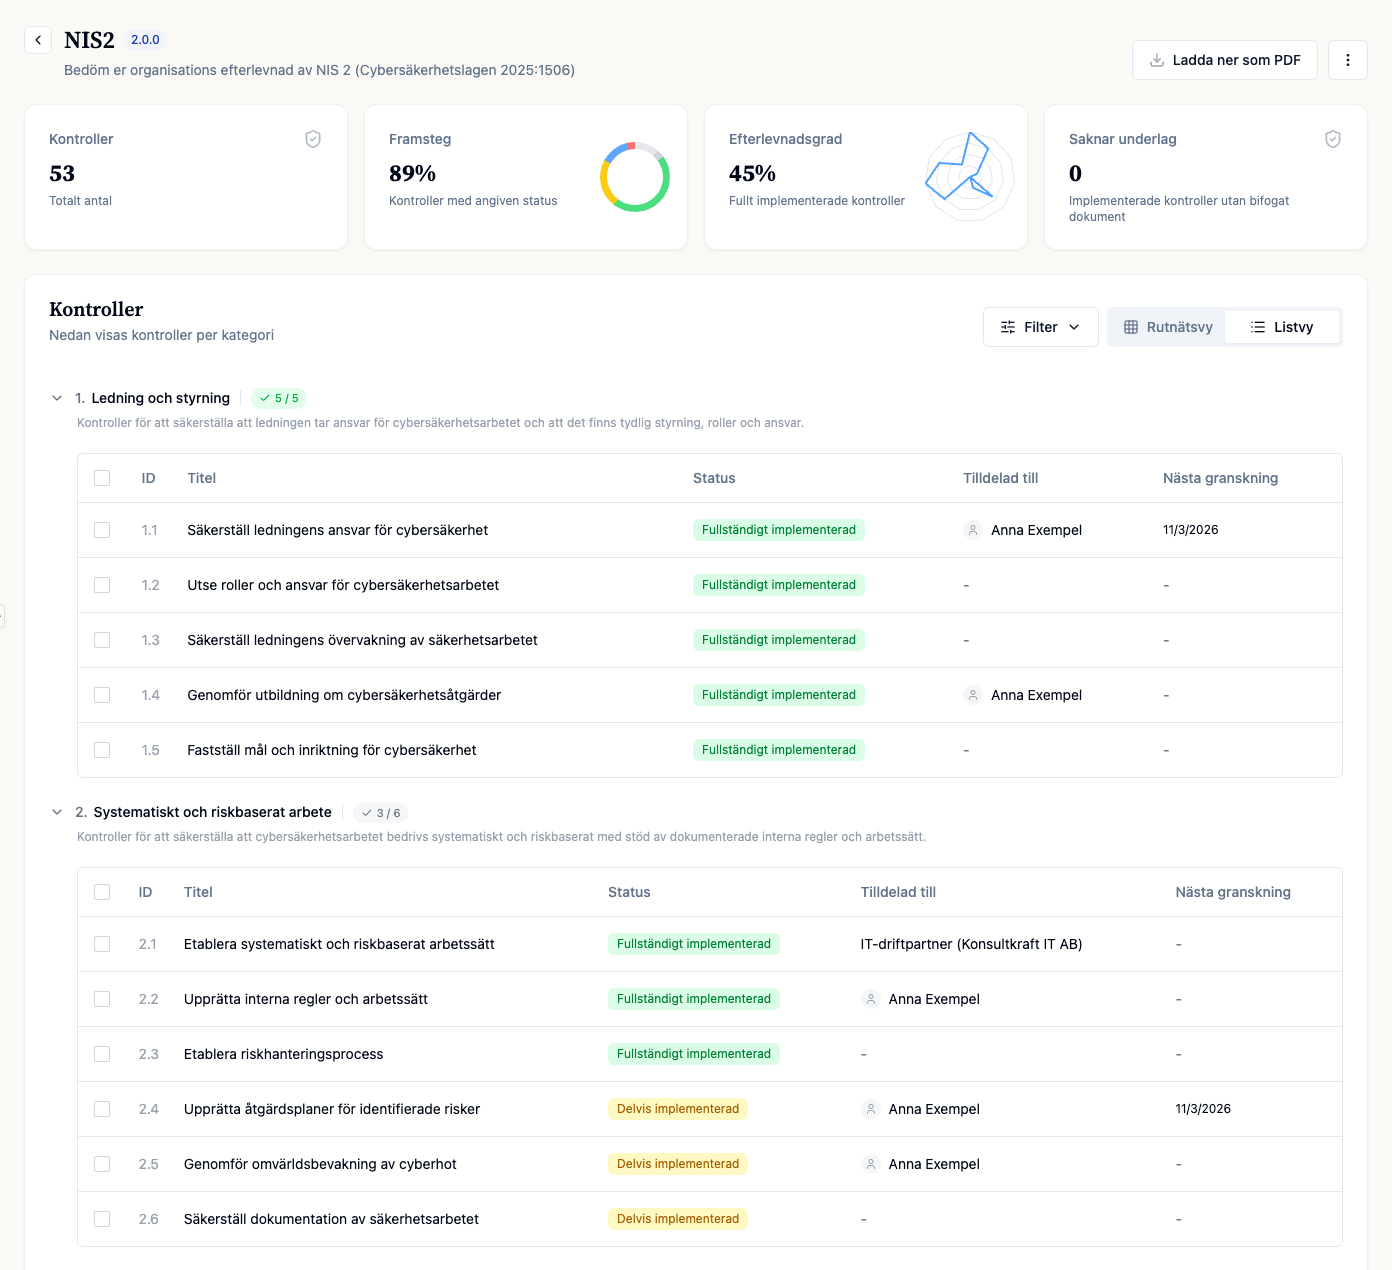
The NIS2 requirements catalogue turns the requirements into controls. Each control has a status, an owner and a next review date, and the actions are followed up there.
Add-on
An asset register with CIA classification, information assets and Article 30 records. Added on top of Risk and requirements, so the assets link to the same risks.
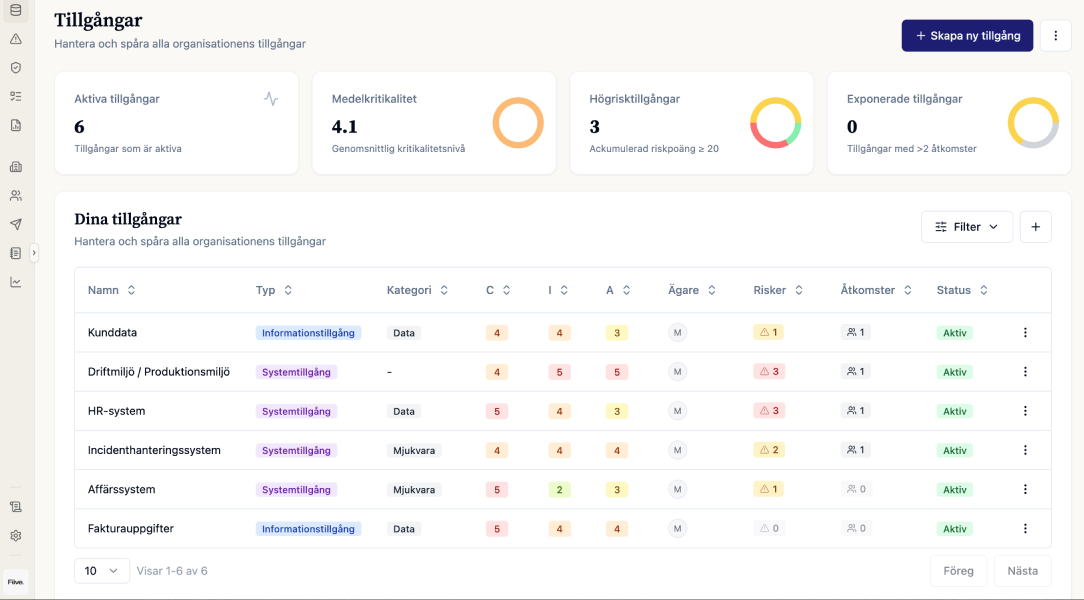



Supplier security assessments at three levels of depth for NIS2 and ISO 27001, a risk register with risk treatment, the NIS2 requirements catalogue and actions linked to risks and requirements. Data protection with an asset register and Article 30 records is available as an add-on.
Yes. Every customer starts with the supplier module. Risk and requirements is added on top, and Data protection on top of Risk and requirements.
Yes, for the parts security work most often needs evidence for: supplier security, the risk register, the NIS2 requirements and the actions, in one system. ChainSec is not an enterprise GRC suite with workflow builders and group structures.
No. ChainSec is not an ISO system and does not replace your management system. We handle specific parts: suppliers, risks, requirements and actions.
Pricing is set per customer based on the parts you need.
30 minutes. We show assessment, risk and action based on the work you do today.