Match the assessment to the supplier
Ready-made assessments for NIS2 and ISO 27001 at three levels. The critical hosting provider gets more questions than the office supplies vendor.
For IT and security
Keep supplier assessments, risks and actions in one system. See what needs follow-up, who owns it and how the work is progressing, even when security work shares your time with daily operations.
Match the assessment to the supplier’s importance and follow up on what needs action. Ownership and status make the next step clear.
Ready-made assessments for NIS2 and ISO 27001 at three levels. The critical hosting provider gets more questions than the office supplies vendor.
Record a deviation from a flagged questionnaire answer and follow up on the supplier’s response and action. For risks and requirements, create actions with an owner, deadline and status.
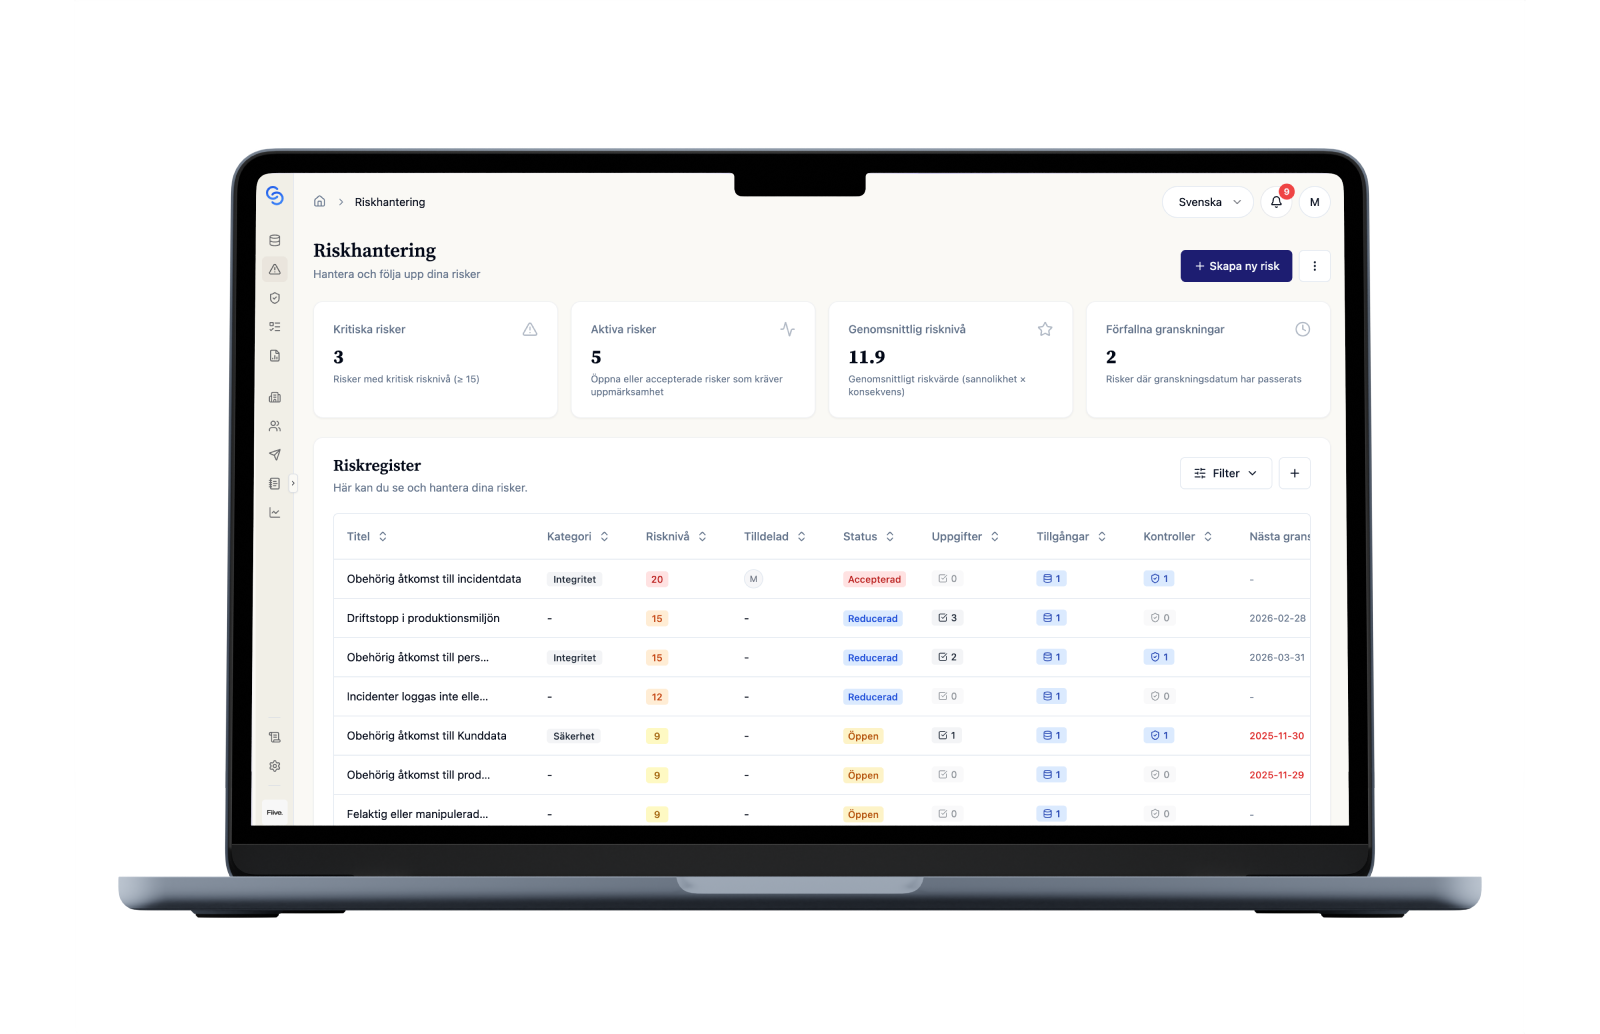
Keep risk assessment and treatment in the risk register. Link risks to requirements and actions so you can follow what you have decided and what remains.
From the first supplier assessment to the next follow-up: answers are collected, gaps get a next step and earlier work stays available when you return.
Choose a security assessment for NIS2 or ISO 27001 at the depth that fits the supplier. Adapt the questions to your needs and send the assessment.
The supplier answers in the form and uploads certificates and policies. You see who has answered.
Record deviations from answers that need follow-up. Assess the risks and create actions for risks and requirements with an owner, deadline and status.
Review open risks and actions and follow up on overdue work. The supplier’s earlier answers and history are available for the next assessment.
When security work shares your time with operations, you need to see where you left off. Answers, owners and status are kept together so you can continue following up or let a colleague take over.
Yes. Ready-made security assessments for NIS2 and ISO 27001 are available at three levels of detail. You choose the assessment that fits the supplier and can adapt the questions, giving a critical hosting provider a more comprehensive assessment than a less important supplier.
A flagged questionnaire answer can become a deviation linked to the supplier. You document the supplier’s response, the action and the result of the follow-up there. In Risk and requirements, you can also link actions to risks and requirements, with an owner, a deadline and a status.
You can use the system to check the status of supplier assessments, open risks and ongoing actions. Earlier assessments and action history provide evidence of what has been done and what needs follow-up.
ChainSec gives you ready-made supplier assessments for NIS2 and ISO 27001, a NIS2 requirement catalog with the ten mandatory security areas, and a traceable history of assessments and actions. Which requirements apply to you, and whether you meet them, is your own assessment.
We start from your work and show how to assess your current position, assign ownership and follow up on actions.